Your network connects employees, systems, servers, devices, branches, suppliers and business-critical applications. ASER's UTM Firewall solution combines multiple layers of protection to control traffic, identify threats and increase visibility into everything entering and leaving the corporate network.
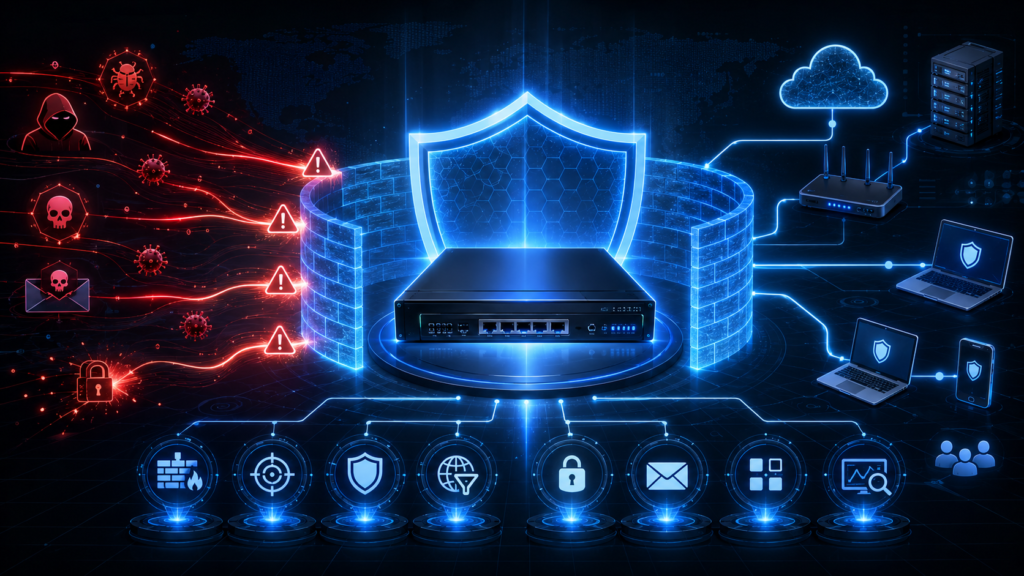
UTM stands for Unified Threat Management.
It is a solution that brings different network security capabilities together in a single platform.
Instead of relying on several isolated tools to control access, filter content, identify attacks and protect connections, a UTM Firewall centralizes these functions and gives a broader view of the environment's security.
The solution can include capabilities such as:
Today's threats don't come through just one network port.
An attack can start with a compromised remote access, a malicious website, an infected file, an unauthorized application or a flaw in an internet-facing service.
That's why protecting the network takes more than simply allowing or blocking connections.
A UTM Firewall adds multiple security mechanisms that analyze traffic and apply protection policies based on the users, applications and risks involved.
With a UTM Firewall, your company can:
Defines which communications can enter or leave the network based on predefined rules. This makes it possible to limit connections, services, protocols and sources that aren't needed for the operation.
Identifies and controls the applications used on the network. The company can set specific rules for cloud storage, communication, social media, remote access and other categories.
The IPS engine monitors traffic for patterns associated with known attacks and vulnerabilities. When it identifies a suspicious attempt, the solution can block the communication before the attack reaches the protected system.
Files and content moving across the network can be analyzed for malicious code. This adds a layer of protection against different forms of malware.
Lets you create policies to control which categories of websites users can access. Besides supporting corporate policies, it helps reduce access to malicious, fraudulent or inappropriate pages.
Security policies can be applied according to different profiles, so administrative areas, technical teams, visitors and suppliers can have different levels of access.
Get a centralized view of connections, users, applications and security events.
Centralize different protection controls in a single architecture.
Create rules that can be applied in a standardized way to different users, networks and sites.
Limit services, applications and communications that don't need to stay available.
Use VPN and authentication policies to protect connections made from outside the company.
Create protected connections between headquarters, branches, offices and other environments.
UTM stands for Unified Threat Management.
The concept consists of bringing different network security mechanisms together in a single solution.
A traditional firewall mainly controls connections and network traffic.
A UTM solution adds other security mechanisms, which may include IPS, antivirus, web filtering, application control, VPN and other capabilities.
The concepts share many functions and, as technology has evolved, the line between the categories has become less rigid.
Both can include advanced inspection and protection mechanisms.
The most suitable architecture should be defined based on the company's needs and the capabilities actually available in the chosen solution.
Depending on the solution and the features enabled, files and traffic can be analyzed by antivirus and anti-malware engines.
This works as an additional security layer and doesn't necessarily replace protection installed on endpoints.
Not necessarily.
Network protection and endpoint protection act at different points of the infrastructure and can work together.
Many UTM solutions include intrusion prevention capabilities.
It analyzes traffic for behavior and patterns related to threats and exploitation attempts.
Book a free assessment and see how Aser takes over the governance of remediation in your operation.