Blocking threats at the entrance is essential. But what happens when an attacker gets past the first barriers?
Compromised credentials, infected devices, legitimate access used maliciously and more sophisticated attacks can generate activity that traditional tools don't block right away.
ASER's NDR solution expands network visibility, analyzes behavior and identifies signals that may indicate compromise, lateral movement, malicious communication or data exfiltration attempts.
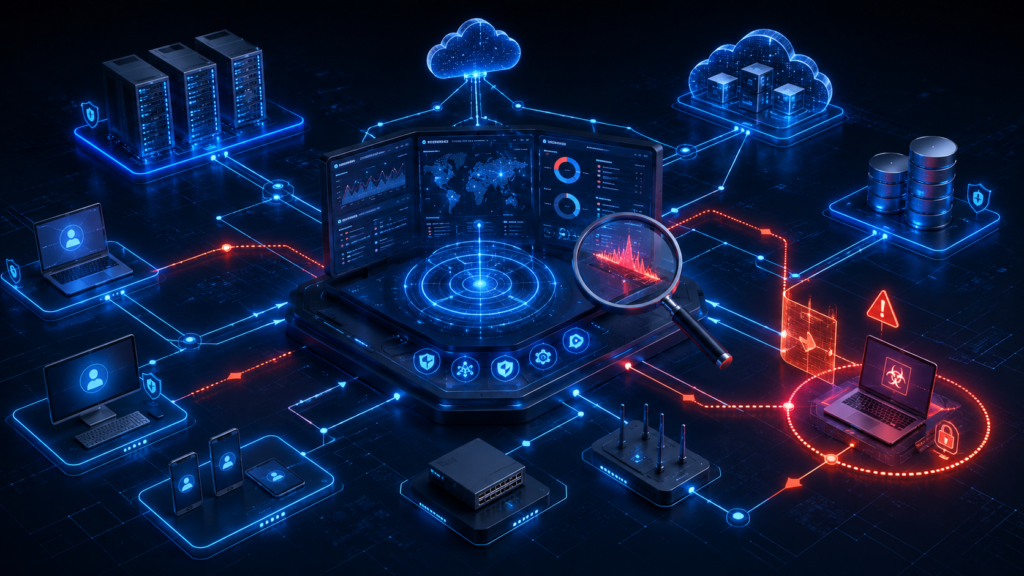
NDR stands for Network Detection and Response.
It is a cybersecurity technology designed to continuously monitor and analyze network traffic for suspicious behavior, anomalies and possible signs of attack.
Unlike controls that only decide whether a connection should be allowed or blocked, NDR seeks to understand how users, devices, servers and systems normally communicate.
When behavior deviates from that pattern, the solution can raise alerts and provide information for investigation.
NDR can help identify:
An organization can have a firewall, antivirus, EDR and other security controls and still be compromised.
That's because attackers also use:
Information about network communications is captured from the points defined in the architecture.
The solution identifies patterns in how devices, users and systems normally communicate.
Relevant changes in these patterns can indicate activity that needs investigation.
Different events and behaviors can be correlated to provide more context about a potential threat.
Alerts can be ranked according to risk, asset criticality and observed behavior.
Security teams use the recorded information to understand the source, destination, sequence of events and possible impact.
An attacker rarely stays on the first compromised device.
After initial access, they may try to reach servers, privileged users and other resources.
NDR helps identify unusual communication patterns that can indicate this movement through the infrastructure.
An infected workstation or server may start communicating differently from its usual behavior.
The solution analyzes these changes and can flag suspicious activity.
Malware and attacker tools can establish connections to external servers to receive instructions or send out information.
NDR can help identify communications that don't match the expected pattern.
Abnormal information transfers can indicate attempts to take data out of the organization.
The analysis considers volume, destination, frequency and other aspects of the traffic.
Once inside the network, an attacker may run scans to discover servers, ports, services and other assets.
These patterns can be detected by analyzing communications.
Legitimate protocols can also be used for malicious activity.
NDR helps identify uses outside normal behavior.
NDR stands for Network Detection and Response.
It is a category of technology that monitors and analyzes network traffic to identify suspicious activity and support threat investigation and response.
A firewall mainly works by applying policies to allow or block communications.
NDR analyzes the behavior of communications across the infrastructure, looking for abnormal or potentially malicious activity.
The technologies are complementary.
No.
NDR adds visibility and detection capabilities, while the firewall still plays a fundamental role in controlling and protecting the network.
EDR monitors activity inside the endpoints where it is installed.
NDR analyzes network traffic between devices and systems.
Together, they offer different perspectives on a potential threat.
No.
One advantage of behavioral analysis is that it helps identify suspicious activity even when it doesn't directly match a known signature.
Network analysis usually doesn't depend on installing an agent on every device.
The architecture and collection mechanisms vary according to the chosen platform.
Book a free assessment and see how Aser takes over the governance of remediation in your operation.