Mobile apps hold personal information, credentials, transactions, corporate data and access to critical services. A vulnerability can enable account takeover, data exposure, feature tampering, interception of communications or unauthorized access to the systems connected to the app.
ASER's Mobile Pentest simulates real attacks against Android and iOS apps to identify vulnerabilities in the app, in its communication with servers, in the APIs and in the mechanisms that protect user data.
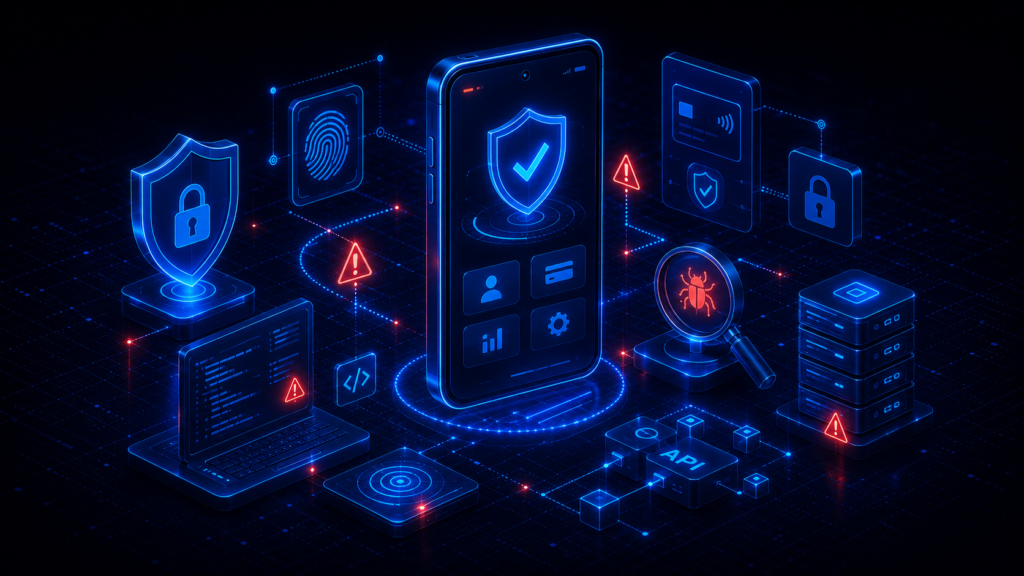
A Mobile Pentest is a penetration test specialized in applications built for mobile devices.
During the engagement, our specialists analyze the app from an attacker's perspective, looking for vulnerabilities that could allow unauthorized access, data exposure, interception of information, feature tampering or compromise of integrated systems.
The test isn't limited to what appears on the app's screen.
The assessment can cover the compiled code, on-device storage, authentication mechanisms, communication with servers, APIs, the libraries used and interaction with Android or iOS features.
Unlike a purely automated analysis, a Mobile Pentest combines specialized tools, static analysis, dynamic analysis, reverse engineering and manual testing by offensive security professionals.
Mobile apps run on devices that aren't under the company's direct control.
The app can be installed on modified devices, run on emulators, inspected with reverse engineering tools or manipulated by malicious users.
In addition, most features depend on APIs and remote services. A flaw in the app or in its communication with these environments can compromise data, accounts, transactions and internal processes.
Tests are carried out by professionals who combine technical analysis, controlled exploitation and knowledge of attacks targeting mobile apps. Team certified in OSCP, CEH and eWPT.
We don't just analyze the app installed on the device. Depending on the scope, we also assess the APIs, remote services, authentication, integrations and other components that keep the solution running.
The methodology is adapted to the characteristics, controls and attack surfaces of each operating system.
We combine inspection of the compiled app with assessment of its behavior at runtime.
We use tools for support, but results are validated and deepened by specialists.
Tests can follow references such as OWASP MASVS, OWASP MASTG, OWASP API Security Top 10 and best practices applicable to the assessed environment.
We map the platforms, versions, environments, APIs, user profiles and features to be assessed.
We set up devices, emulators, proxies, instrumentation tools and other resources needed for the assessment.
We identify technologies, libraries, components, permissions, endpoints, authentication mechanisms and possible attack surfaces.
We inspect the compiled app, its settings, its components and the protection mechanisms in place.
We run the app in a controlled environment to assess its behavior, communication, data storage and interaction with the device.
Specialists validate the findings and exploit vulnerabilities in a controlled way to prove risks and identify possible impacts.
No test starts without formal authorization from the environment owner. Out-of-scope systems are never touched.
Assets, techniques, time windows and what is excluded are recorded before we start, so there are no surprises.
If there is unexpected impact or any sign of a real incident in progress, testing stops and you are notified right away.
One person in charge at ASER and one at the customer, with a direct escalation channel throughout the engagement.
We collect only what is needed to prove each finding, with agreed retention and disposal periods.
After fixes are applied, a retest confirms that each flaw has really been eliminated, when included in the scope.
Where are my weaknesses and which should I fix first? Continuous scanning, risk-based prioritization and remediation governance.
Is this flaw exploitable, and what is the impact? Controlled exploitation of applications and APIs, with evidence and a remediation plan.
How far can an intruder get in my network? Internal and external infrastructure testing, segmentation and lateral movement.
Does my team detect and respond to a real attack? Adversary simulation with defined objectives, measuring detection and response.
What do I have exposed on the internet without knowing? Continuous discovery of exposed assets, services and domains.
Do my employees fall for scams? Phishing, SMS and phone-call simulations, with training at the moment of failure.
A Web Application Pentest assesses systems accessed through browsers.
A Mobile Pentest considers characteristics specific to Android and iOS apps, such as on-device storage, permissions, native components, inter-app communication, reverse engineering and tampering with the installed file.
When the app uses APIs, those services can also be included in the scope.
Not necessarily.
Depending on the scope, the assessment can include the app, its APIs, authentication mechanisms, servers and the integrations used by the solution.
No.
A Mobile Pentest can be performed from the app's compiled file.
Access to source code, architecture or documentation can be provided in White Box assessments to increase test depth and coverage.
For Android, an APK or AAB file, or a version installed through a testing channel, can usually be provided.
For iOS, access can be through an IPA file, TestFlight, internal distribution or another method agreed in advance.
The exact requirements are set during scoping.
No.
The Pentest can be performed before publication, using development, staging or restricted-distribution builds.
anfona
We can assess how the app behaves on rooted or jailbroken devices and whether the controls in place can be bypassed.
The need for and depth of these tests depend on the application's risk and context.
Talk to a specialist to define the scope of your test and receive a proposal.