Most companies don't know what is exposed on the internet. Forgotten subdomains, misconfigured cloud services, expired SSL certificates, shadow IT and fake domains (typosquatting) create an invisible attack surface that attackers exploit every day. ASER maps, monitors and reduces your external exposure in real time.
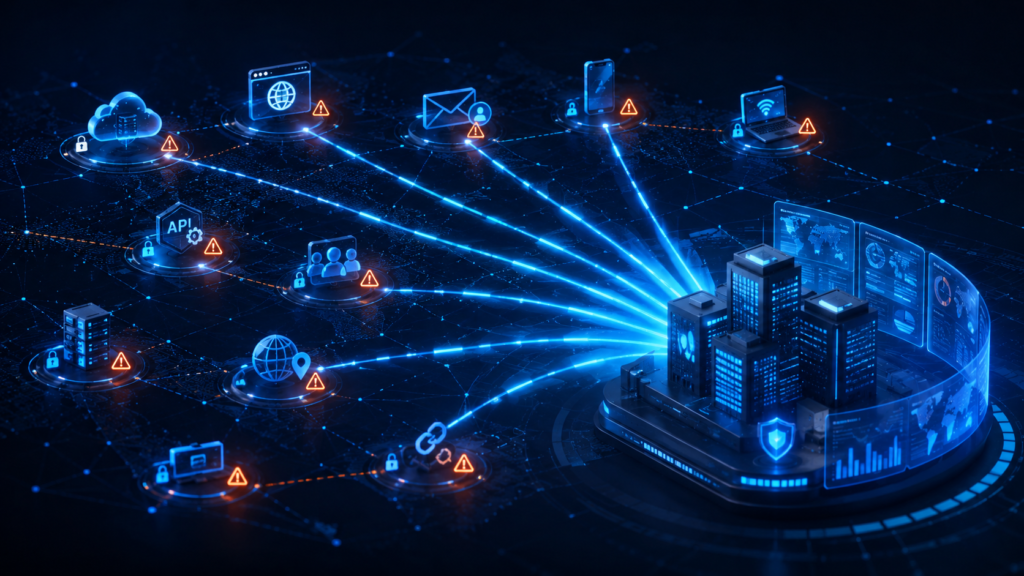
External Attack Surface Management (EASM) is the practice of continuously discovering, inventorying, assessing and monitoring every IT asset that is exposed to the internet and may be targeted by attackers. Unlike a one-off pentest, EASM operates 24 hours a day, 7 days a week, scanning the company's external attack surface for:
EASM complements other disciplines such as CSPM (Cloud Security Posture Management), CAASM (Cyber Asset Attack Surface Management) and VM (Vulnerability Management), forming a unified view of the organization's exposure.
The external attack surface grows exponentially. Every new cloud service, API, integrated partner or acquisition adds assets the security team can't see. Without visibility, you can't protect.
Our scanners map subdomains, IPs, ranges, certificates, technologies and exposed services, with recurring scans to find new assets as soon as they appear.
We identify applications, APIs, S3 buckets and databases created by business teams without security approval. You see what your own employees forgot to report.
We track domain variations that imitate your brand. Get alerts when attackers register domains for phishing, before your customers are deceived.
We don't flood you with thousands of alerts. Each vulnerability is prioritized considering exposure, asset criticality, presence of sensitive data and likelihood of exploitation.
We integrate AWS, Azure, GCP and on-premise environments. See your entire attack surface in a unified dashboard, with filters by business unit, application or criticality.
Unmanaged assets are decommissioned, vulnerabilities are fixed and shadow IT is formalized, with progress tracked month by month.
Complete inventory of subdomains, IPs, ranges, SSL certificates, exposed services and technologies detected on the internet. Continuously updated with newly discovered assets.
Identification of unauthorized cloud services, applications and APIs created by internal teams. Mapping of AWS, Azure and GCP resources outside security control.
Tracking of look-alike domains used for phishing, fraud and social engineering campaigns. Real-time alerts on suspicious new registrations.
Continuous CVE scanning of exposed services. Prioritization by criticality, availability of public exploits and business impact. Reports with proof of concept and remediation.
Assessment of cloud configurations: public S3 buckets, open security groups, permissive IAM, exposed databases. Aligned with CIS AWS/Azure/GCP Foundations.
Executive dashboard with exposure trends, monthly comparison, remediation SLA and risk-reduction ROI. Exportable for board presentations and audits.
Domains, brands and IP ranges are confirmed with you before we start. Third-party assets are never scanned without authorization.
We use public sources and lightweight scans, with no exploitation and no impact on operations.
Specialists review findings before alerting, to reduce false positives.
Each exposure comes with the risk, the affected asset and the recommended action for the right owner.
We collect and keep only what is needed to prove each exposure.
Critical exposures become a remediation plan in Vulnerability Management or are validated in a penetration test.
Where are my weaknesses and which should I fix first? Continuous scanning, risk-based prioritization and remediation governance.
Is this flaw exploitable, and what is the impact? Controlled exploitation of applications and APIs, with evidence and a remediation plan.
How far can an intruder get in my network? Internal and external infrastructure testing, segmentation and lateral movement.
Does my team detect and respond to a real attack? Adversary simulation with defined objectives, measuring detection and response.
What do I have exposed on the internet without knowing? Continuous discovery of exposed assets, services and domains.
Do my employees fall for scams? Phishing, SMS and phone-call simulations, with training at the moment of failure.
EASM (External Attack Surface Management) is a continuous process of discovering and monitoring internet-exposed assets, while a pentest is a one-off, manual assessment. EASM operates 24/7, detecting new assets, shadow IT and vulnerabilities in real time, complementing — not replacing — the pentest.
The initial mapping takes a few days, depending on the size of the infrastructure. After that, monitoring is continuous, with recurring scans that find newly exposed assets.
Yes. Our scanners detect cloud services, APIs, applications and resources created without formal security approval — including in non-centralized AWS, Azure and GCP accounts. This is one of the main EASM use cases.
No. EASM complements CSPM, CAASM and Vulnerability Management. While CSPM focuses on cloud configurations and VM on known vulnerabilities, EASM brings external visibility — what is exposed on the internet and reachable by attackers.
We track domain variations that imitate your brand (e.g. your-domain.com vs. your-domain.net, your-domain-br.com). When a suspicious domain is registered, you get an immediate alert with a risk analysis, allowing legal action or takedown before it is used for phishing.
Indirectly, yes. LGPD and ISO 27001 require asset control and risk management. Without knowing what is exposed, it's impossible to demonstrate control. EASM provides the inventory and evidence auditors and regulators expect to see.
Schedule an initial mapping of your external attack surface.