A vulnerable e-commerce site can expose customer data, allow price and discount manipulation, enable fraud, compromise accounts and disrupt one of the company's most important operations: sales.
ASER's E-commerce Pentest simulates real attacks against the online store to identify technical vulnerabilities and business logic flaws across the entire shopping journey, from customer sign-up to payment confirmation.
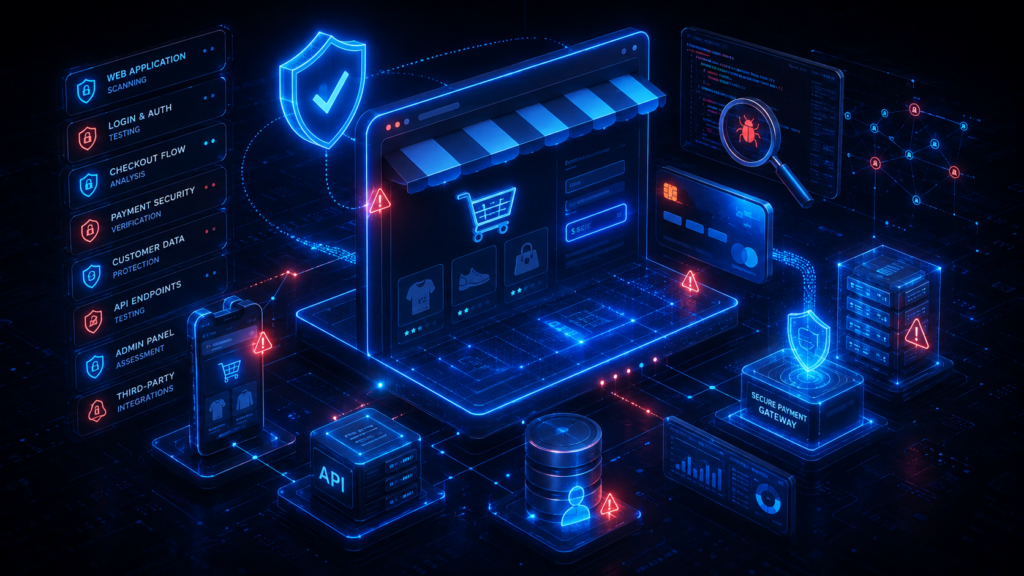
An E-commerce Pentest is a penetration test specialized in online stores, sales platforms and applications connected to the shopping journey.
During the engagement, our specialists take the attacker's perspective and try to exploit vulnerabilities that could allow unauthorized account access, order tampering, price changes, data exposure, coupon abuse or compromise of integrations.
Unlike an automated vulnerability scan, a pentest combines specialized tools, manual testing and knowledge of the e-commerce business processes.
Beyond the technology, we assess the logic that supports the operation.
An e-commerce platform brings together personal data, business information, integrations, payment methods and processes that directly drive the company's revenue.
A seemingly simple vulnerability can be combined with other flaws and used to commit fraud, access customer information, tamper with orders or compromise integrated systems.
Tests are carried out by professionals who analyze the application from an attacker's perspective, combining automated techniques with manual exploitation. Team certified in OSCP, CEH and eWPT.
We don't just check technical vulnerabilities. We analyze how a flaw could affect sales, customers, payments, inventory, reputation and business continuity.
Execution can follow references such as the OWASP Web Security Testing Guide, OWASP Top 10, OWASP API Security Top 10 and best practices applicable to the assessed environment.
We assess scenarios specific to the operation, such as price manipulation, coupon abuse, order tampering and unauthorized access to commercial flows.
Each project is planned according to the architecture, technologies, integrations and features used by the e-commerce platform.
We agree in advance on scope, schedules, credentials, restrictions and rules of engagement to reduce risks to platform availability.
We map the environments, domains, APIs, access profiles, integrations and features to be assessed.
We identify technologies, endpoints, exposed surfaces, authentication flows, integrations and possible entry points.
We use specialized tools to support the initial discovery of vulnerabilities, misconfigurations and exposed components.
Specialists validate the findings and perform manual testing of exploitation, authorization, authentication, sessions, APIs and business logic.
Each vulnerability is analyzed considering how exploitable it is and its technical and business impact on the company.
We deliver the results in a structured way, with an executive view, technical details, evidence and remediation guidance.
No test starts without formal authorization from the environment owner. Out-of-scope systems are never touched.
Assets, techniques, time windows and what is excluded are recorded before we start, so there are no surprises.
If there is unexpected impact or any sign of a real incident in progress, testing stops and you are notified right away.
One person in charge at ASER and one at the customer, with a direct escalation channel throughout the engagement.
We collect only what is needed to prove each finding, with agreed retention and disposal periods.
After fixes are applied, a retest confirms that each flaw has really been eliminated, when included in the scope.
Where are my weaknesses and which should I fix first? Continuous scanning, risk-based prioritization and remediation governance.
Is this flaw exploitable, and what is the impact? Controlled exploitation of applications and APIs, with evidence and a remediation plan.
How far can an intruder get in my network? Internal and external infrastructure testing, segmentation and lateral movement.
Does my team detect and respond to a real attack? Adversary simulation with defined objectives, measuring detection and response.
What do I have exposed on the internet without knowing? Continuous discovery of exposed assets, services and domains.
Do my employees fall for scams? Phishing, SMS and phone-call simulations, with training at the moment of failure.
A scan uses automated tools to identify possible vulnerabilities and misconfigurations.
A pentest goes further. Specialists manually validate the findings, exploit combinations of flaws and analyze scenarios specific to the operation, including authentication, permissions and business logic.
Tests are planned to reduce the risk of downtime. Before starting, we define rules of engagement, schedules, limits, critical systems and stop procedures.
Potentially destructive tests, or those that could compromise the operation, are only performed with prior authorization.
We can assess the implementation of the integration between the e-commerce platform and the gateway, including parameters, callbacks, webhooks, validations and communication flows.
The provider's internal infrastructure can only be tested with formal authorization and specific inclusion in the scope.
Yes. Business logic testing can assess changes to prices, quantities, discounts, coupons, shipping, credits, cashback and other commercial rules used by the platform.
Yes. In the Gray Box model, users with different access levels can be provided, such as customer, seller, operator, partner and administrator.
This makes it possible to check whether permissions are correctly separated.
The service can support the identification and remediation of vulnerabilities related to the payment environment and generate evidence for compliance processes.
However, PCI DSS compliance depends on the scope, architecture, payment processing model and the requirements applicable to the organization. A pentest alone is not a certification
The test can identify vulnerabilities that expose personal data or allow unauthorized access to customer information.
Full LGPD compliance, however, also involves legal, administrative, procedural and governance aspects that go beyond technical testing.
The timeline depends on the size of the platform and the number of features, APIs, integrations, user profiles and environments included.
Duration and schedule are defined after the scoping stage.
Talk to a specialist to define the scope of your test and receive a proposal.