Defensive Pillar - NDR - Network Detection and Response
NAC: control who and what can access your company's network
Identify users and devices, apply access policies and reduce the risk of unauthorized connections
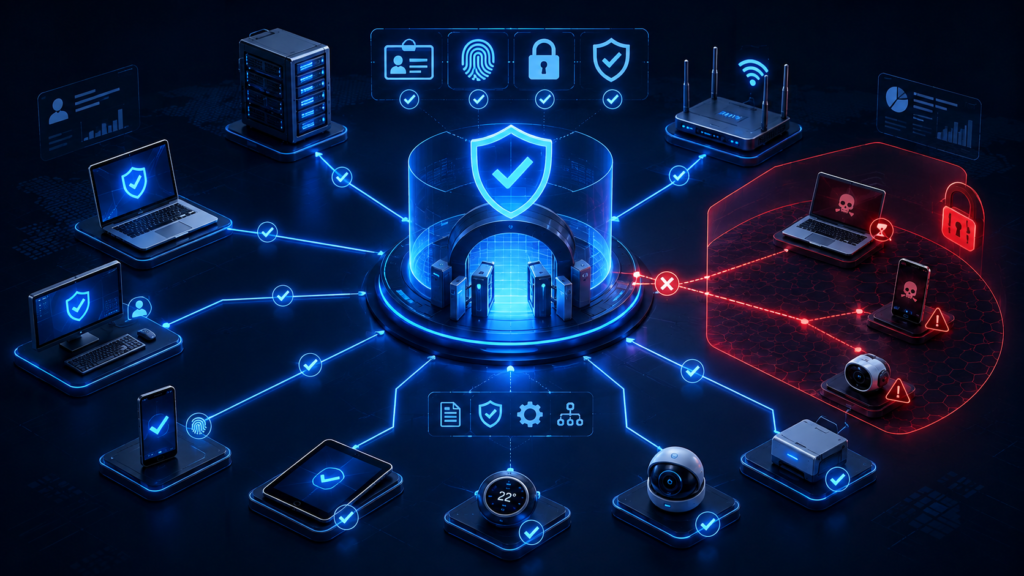
Corporate laptops, smartphones, personal devices, IoT devices, suppliers, visitors and unknown assets can connect to the infrastructure every day. ASER's NAC solution identifies who is connecting, recognizes the devices being used and applies access policies based on identity, profile, device type and security requirements.
It is a technology designed to control which users and devices can connect to the corporate infrastructure and which resources they can access once connected.
Before or during access, the solution can check different information about that user or device and automatically apply the matching security policy.
The goal is to answer fundamental questions:
Who is trying to get in?
Which device is being used?
Does this device meet the security requirements?
Which resources does it really need to access?
Based on this information, NAC can allow, restrict, redirect or block the connection.
Do you know everything that is connected to your network right now?
As infrastructures expand, it has become increasingly difficult to manually control every connected device.
A corporate environment can include equipment managed by IT and many others that aren't under the same level of control.
Among them:
Personal smartphones
Supplier laptops
Printers
Cameras
Sensors
IoT devices
Industrial equipment
Legacy systems
Temporary devices
Unknown equipment
Why Aser
Why choose the NAC at ASER?
Identification
When a user or device tries to connect, the solution collects information to identify who or what is requesting access.
Device classification
The device can be classified by characteristics such as type, operating system, profile and ownership.
Authentication
When required, the user or device goes through authentication mechanisms before being granted access.
Context assessment
The solution considers relevant information to determine which policy should be applied.
Security posture check
Depending on the technology and the policy in place, NAC can check whether the device meets the requirements set by the organization.
Policy enforcement
Based on this information, access can be granted, limited or blocked.
Find out what is really connected to your infrastructure
How does NAC?
01
Device visibility
Know which assets are connected to the infrastructure.
02
User control
Apply different policies based on identity and role.
03
Fewer unauthorized accesses
Prevent unknown devices from getting unrestricted network access.
04
Dynamic segmentation
Route users and devices to environments that fit their profile.
05
Third-party control
Limit suppliers to the resources they really need.
06
BYOD security
Set specific policies for personal devices.
Aser Specialists - Since 2004
Strategic cybersecurity to protect what keeps your business moving