
IKEA, a Swedish multinational furniture and home goods company, faced a complex problem to solve.
The company is falling victim to phishing, and cybercriminals are using the company's internal emails to send fake messages to other employees and gain access to data.
These emails could appear to have been sent by people they worked with, from an external conversation or even from an existing thread.
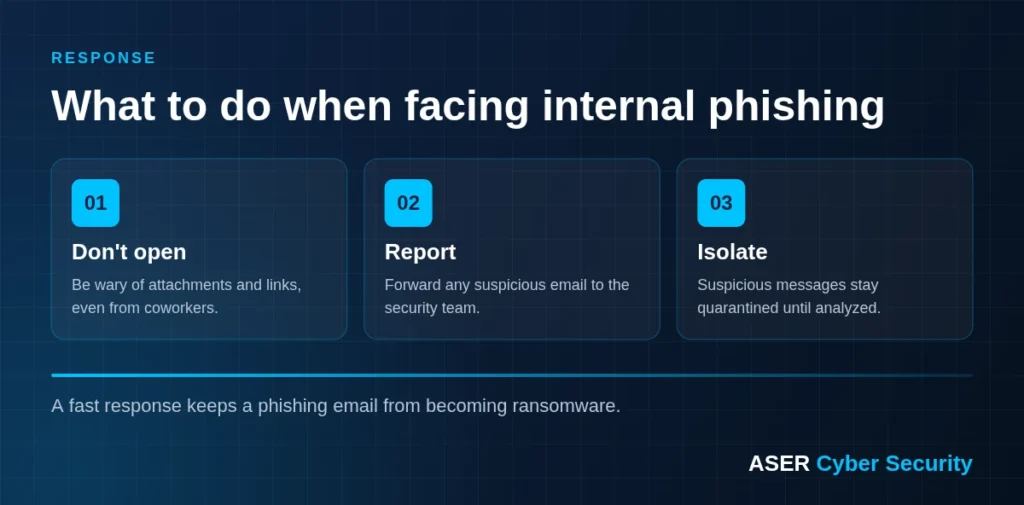
Because the situation was so complex, employees, partners and suppliers were told not to open any incoming email, since a way to resolve the situation had not yet been found.
They were also told to immediately forward any question or suspicion about an email to the experts.
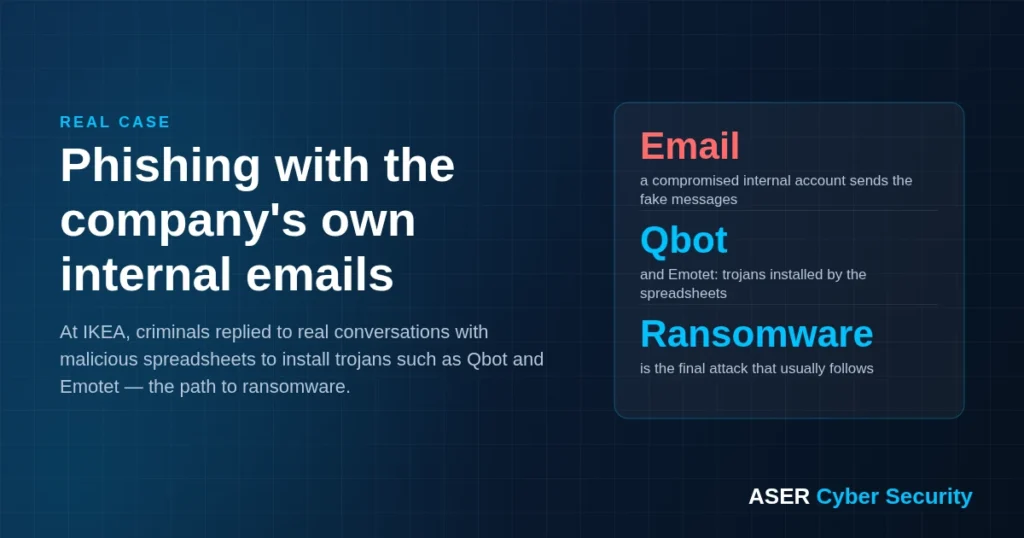
With this attack, IKEA became more vulnerable to a ransomware attack.
The main goal of these hackers with this phishing campaign is to install trojans such as Qbot and Emotet.
Therefore…
Cybercriminals manage to send malicious spreadsheets disguised as legitimate Excel spreadsheets, making it even more likely for this attack to turn into a ransomware attack.
Once these trojans are installed, it is only a matter of time before hackers decide to launch a final ransomware attack, compromising the entire internal network and the sensitive information stored on it.
Would your employees recognize this scam?
The ASER Phishing Platform simulates campaigns like this one and trains the team to identify and report suspicious emails.
For now, in addition to being warned not to open any email, employees were also prevented from removing emails from “quarantine”, to avoid accidents.
As IKEA's own management told its employees, partners and suppliers, it is extremely important that this situation be treated as a priority, and following the protocols provided is necessary to avoid damage.
Forwarding any suspicious email to the experts via Teams to resolve these issues as soon as possible.
This is to prevent data from being stolen and misused by criminals.
Always being aware of what to do to stay secure and avoid these types of attacks is important.
Failures in security caused by cybercriminals are becoming increasingly common.
To keep your company from falling victim to these types of attacks, it is important to have a system that analyzes and identifies any kind of security flaw on the network.
Aser Security is a CEH (Certified Ethical Hacker) certified company by EC-Council. Its Vulnerability Assessment and PenTest services therefore follow the main international information security standards.
Talk now to one of our specialists and find out the best solutions to protect your business.
Is your company prepared against phishing?
For more than 20 years, ASER has protected Brazilian companies with 100% managed security. Talk to an expert and get a free assessment of your business risks.